The brain for
your SecOps stack
Spectrum researches the threats that matter, engineers the data and detections to catch them, and keeps your whole SecOps stack healthy as it changes.
Get startedHow Spectrum works
Inputs
Included
 Threat Discovery
Bring your own
Optional- Red Team reports
- Threat Intelligence
- Threat Models
Threat Monitoring & Research
Data Engineering & Integration
Detection & Response Engineering
Your SecOps stack
Data pipeline
OptionalWorks with


- and more
SIEM
Works with


- and more
Response
OptionalWorks with


- and more
Threats that matter, detected in time
New threats translated into your environment the day they land, and maintained as things change.
 Automatically research threats to understand tradecraft and detection requirements.
 Research every threat against your environment and telemetry, not a generic template
 Go from coverage gap to production-grade detection in 30 minutes
Threats that matter, detected in time
New threats translated into your environment the day they land, and maintained as things change.
- Automatically research threats to understand tradecraft and detection requirements.
- Research every threat against your environment and telemetry, not a generic template
- Go from coverage gap to production-grade detection in 30 minutes
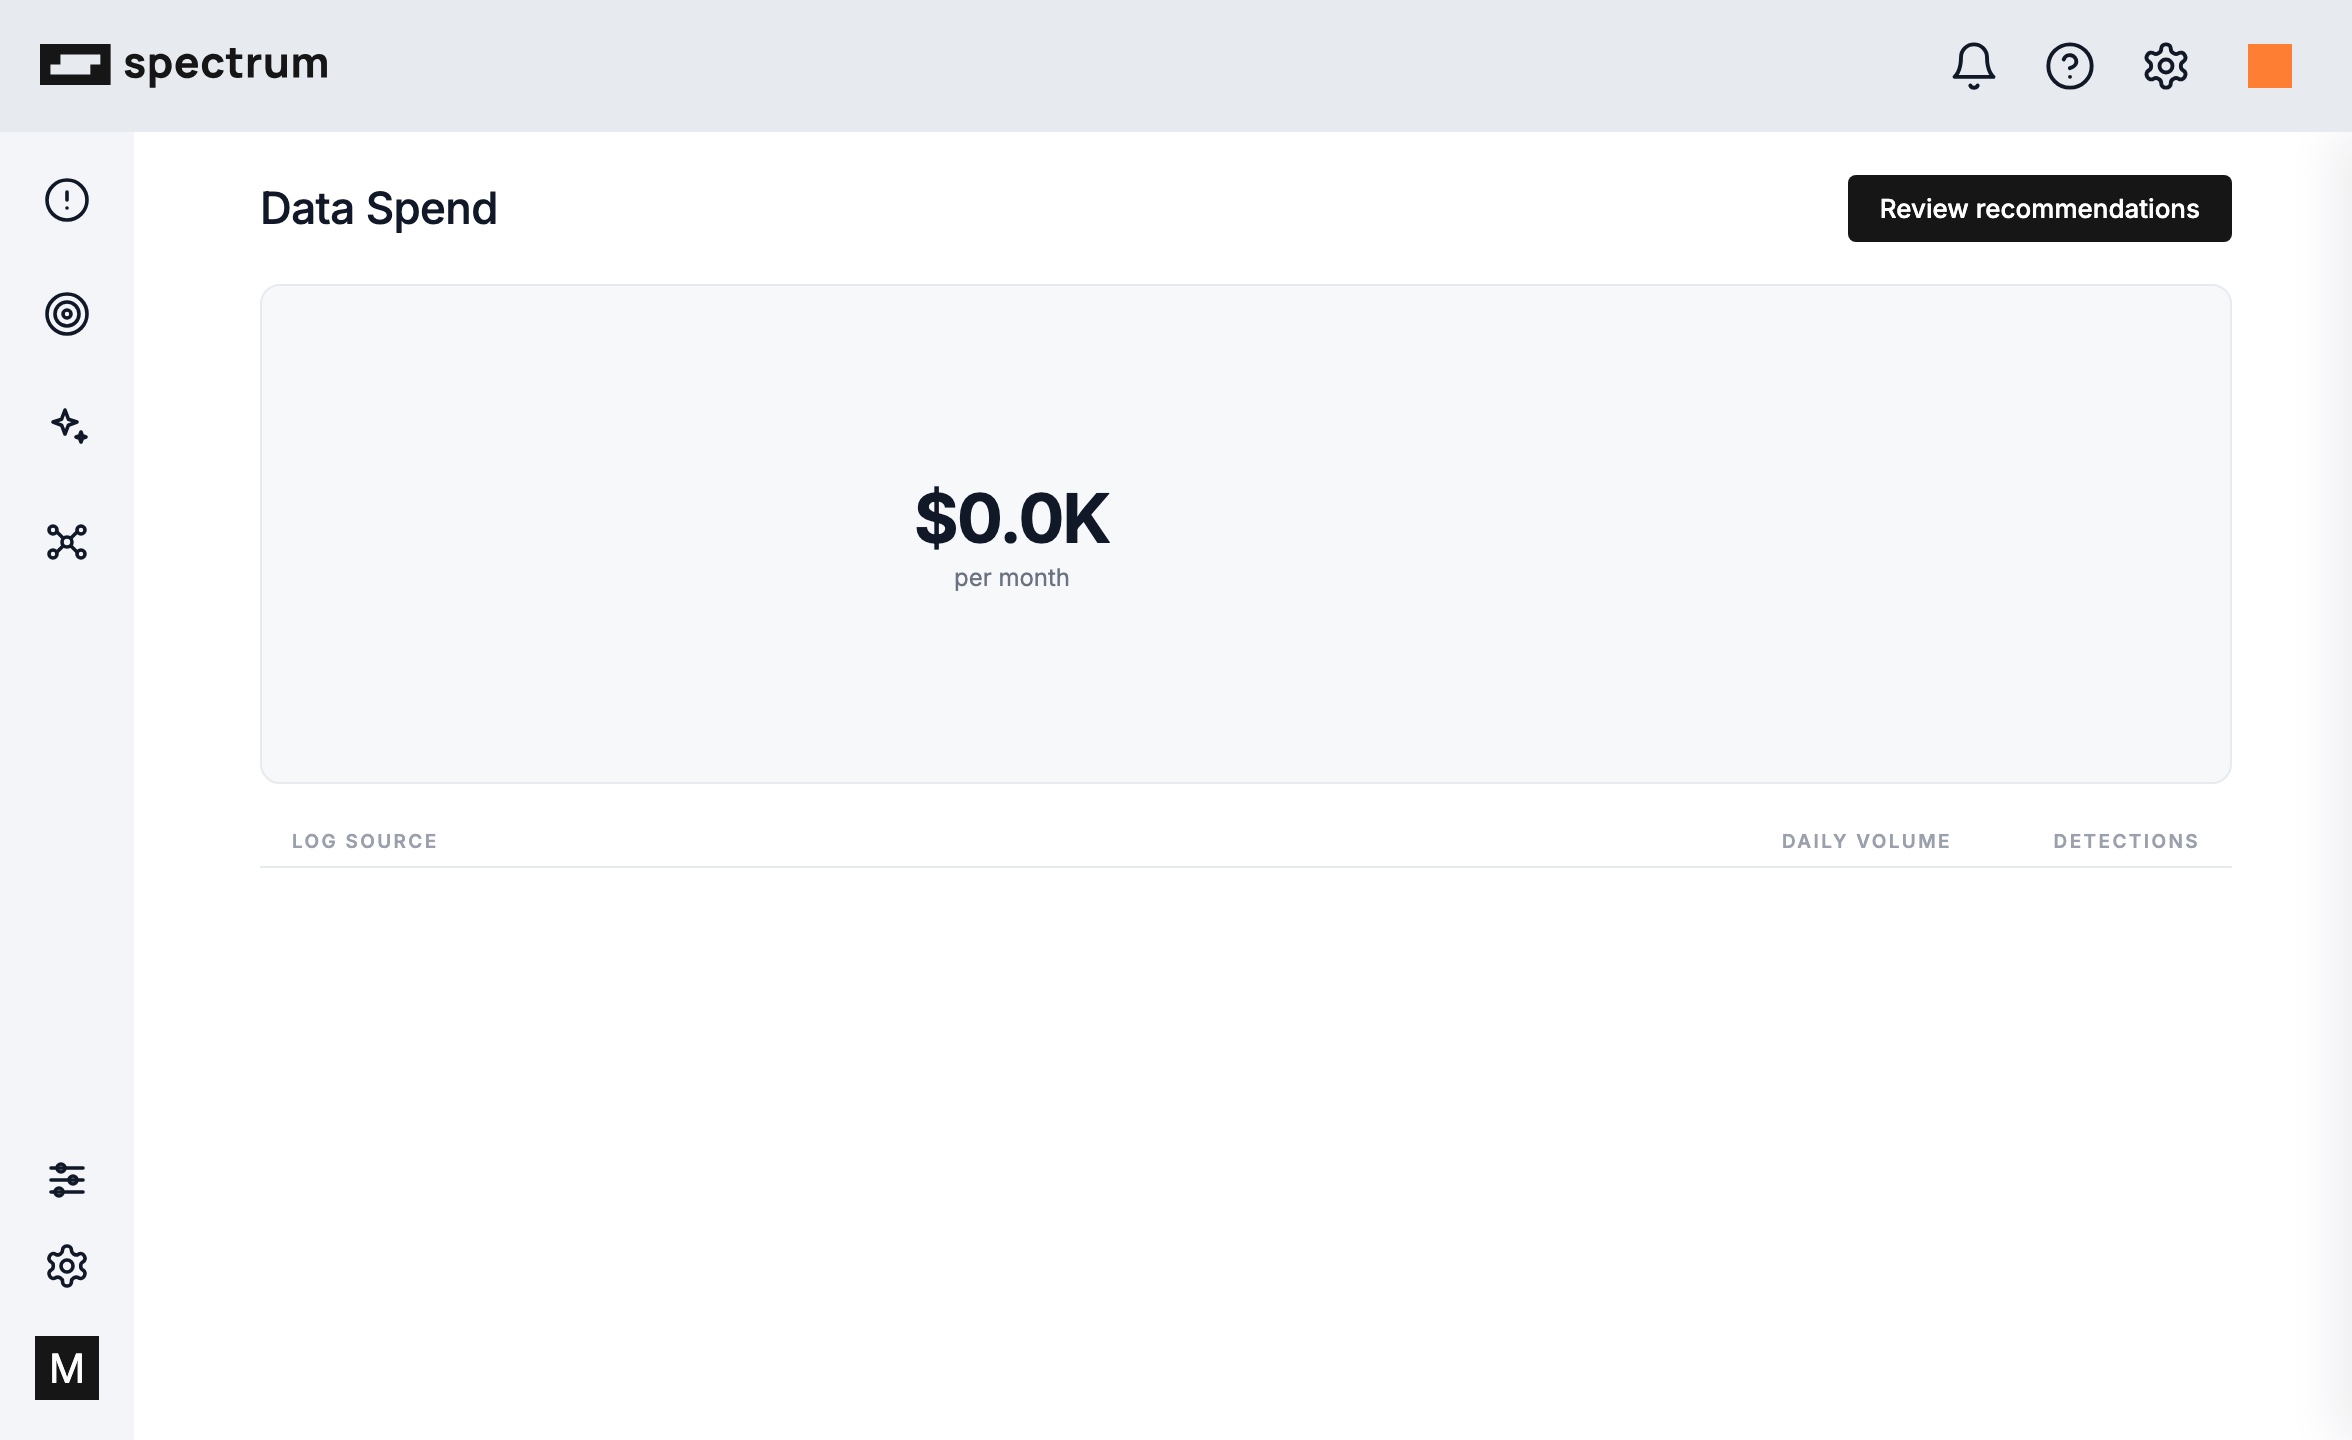
Stop paying for data you aren’t using
Every source and field is tied to a SecOps need, with unused data flagged for removal.
 Let your actual SecOps define which data you keep, which goes to cold storage, and which you stop collecting
 Work through it source by source, with your pipeline tools doing the filtering
 Cut SIEM spend by up to 47% without losing coverage
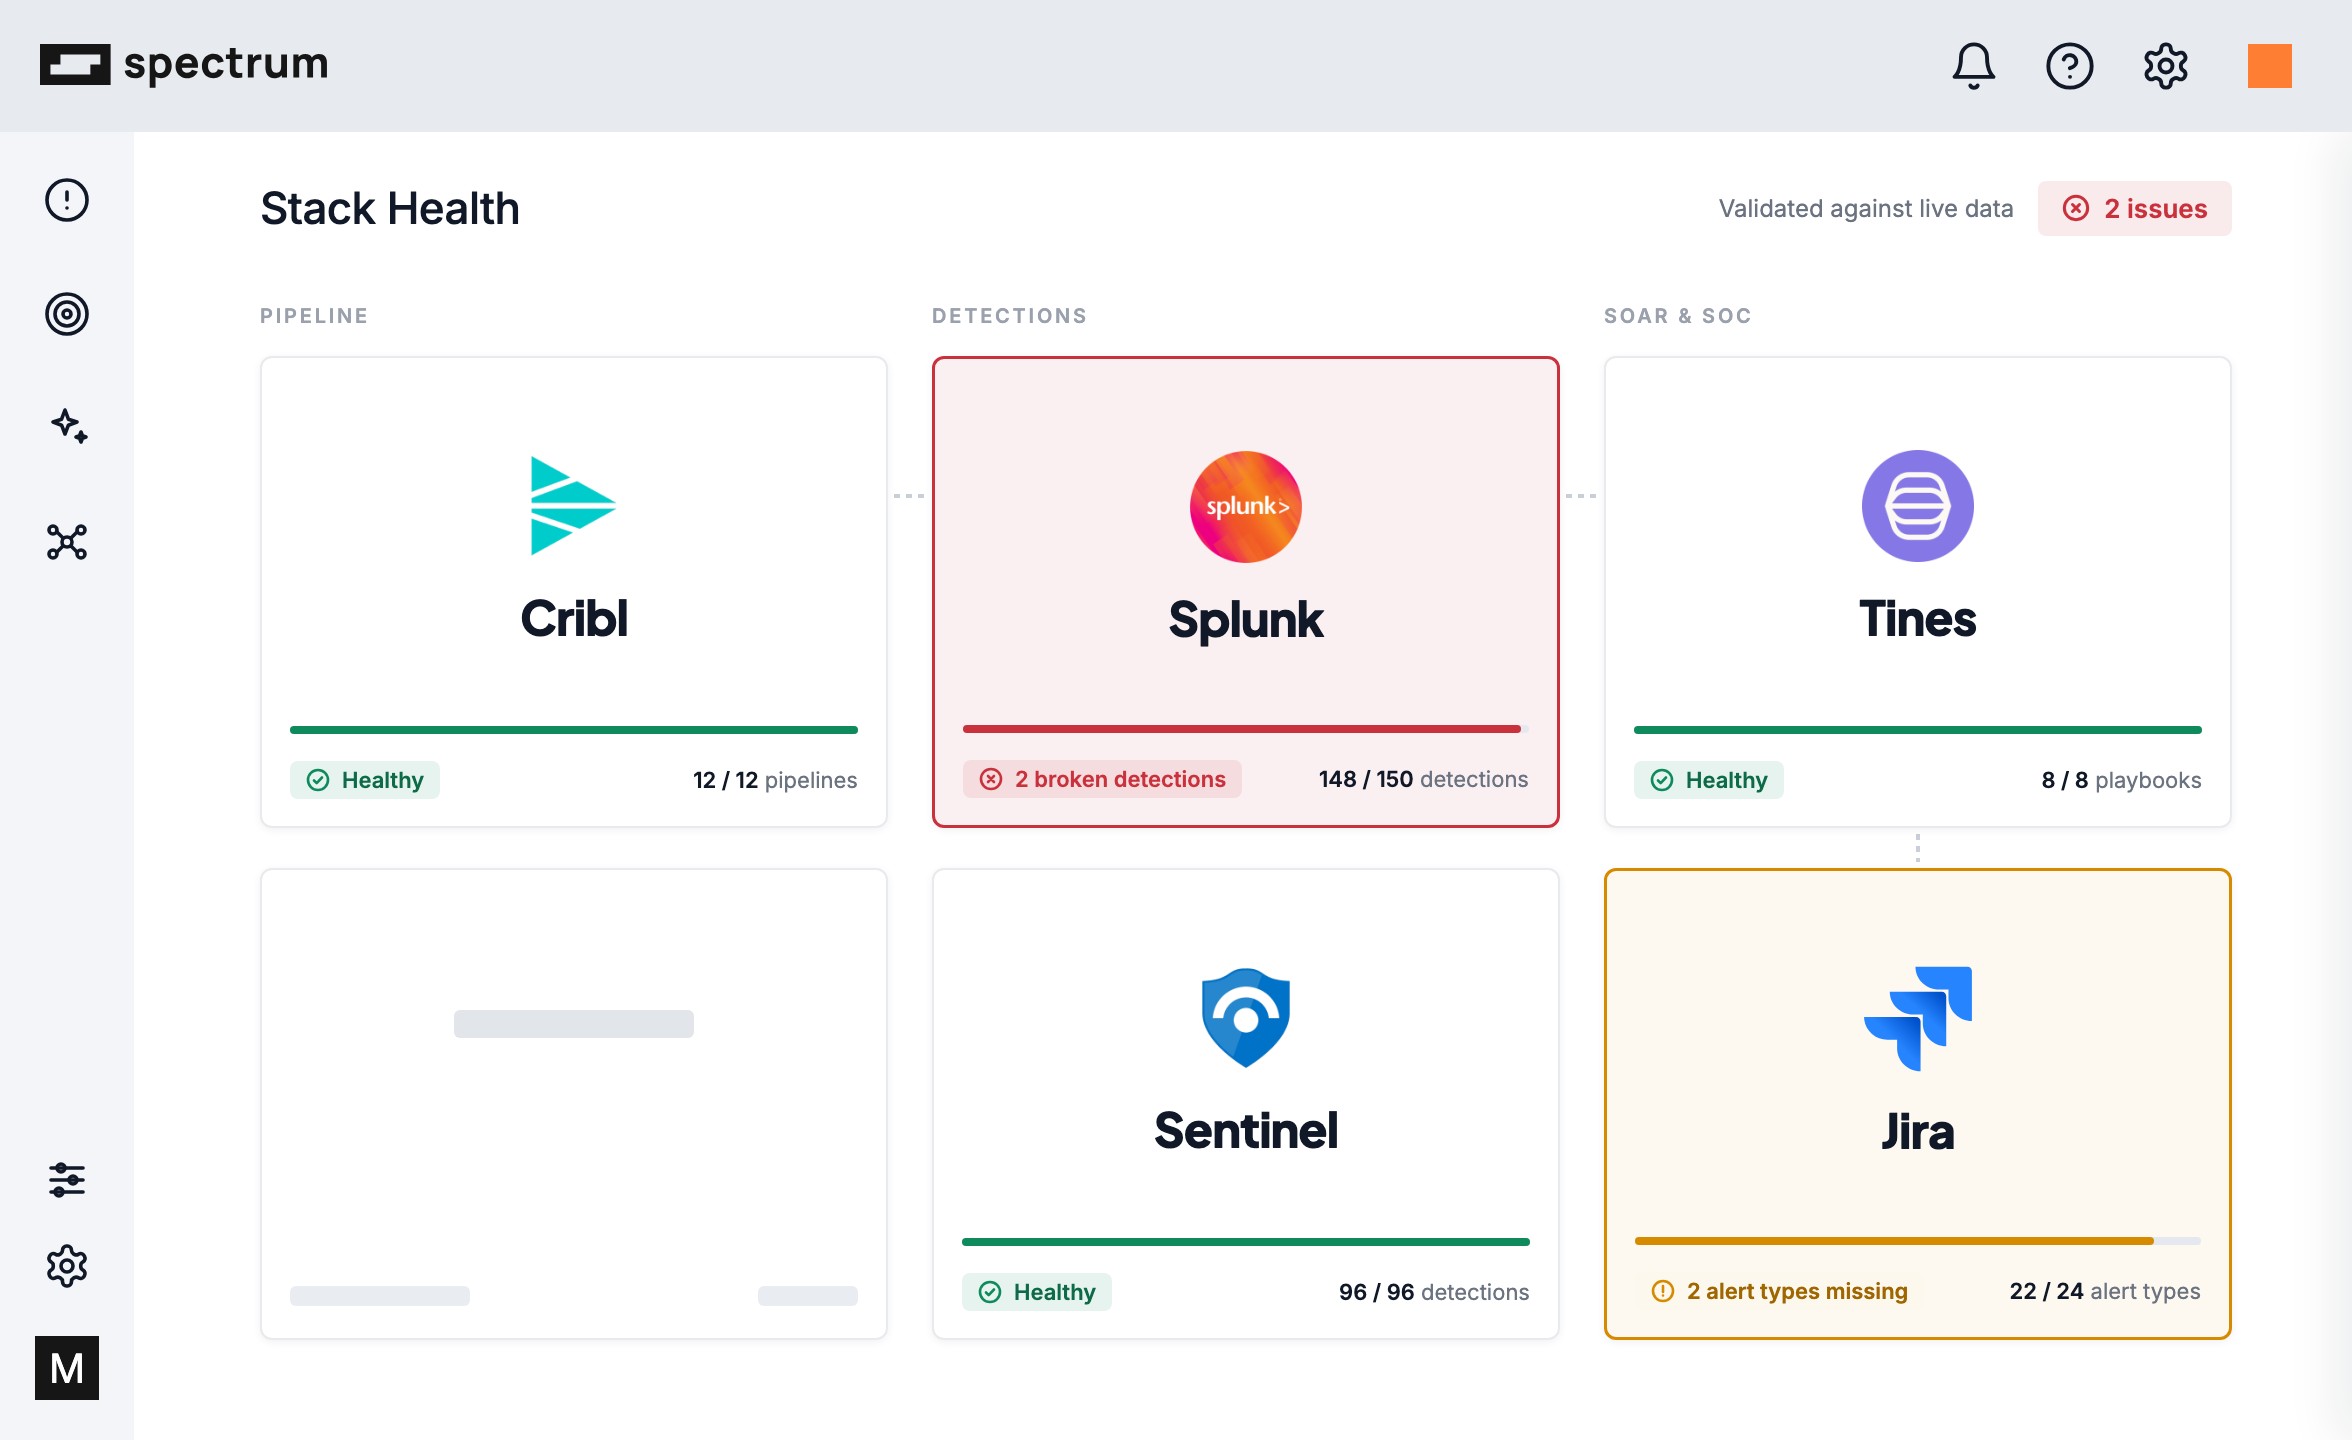
Resilient Security Operations
Stay healthy and resilient without needing to rip & replace.
 End-to-end SecOps health: know the right data is making it to the right places, and that your detections are alive and well
 29% of your detections could be broken: every one is checked against live data, and fixed when it breaks
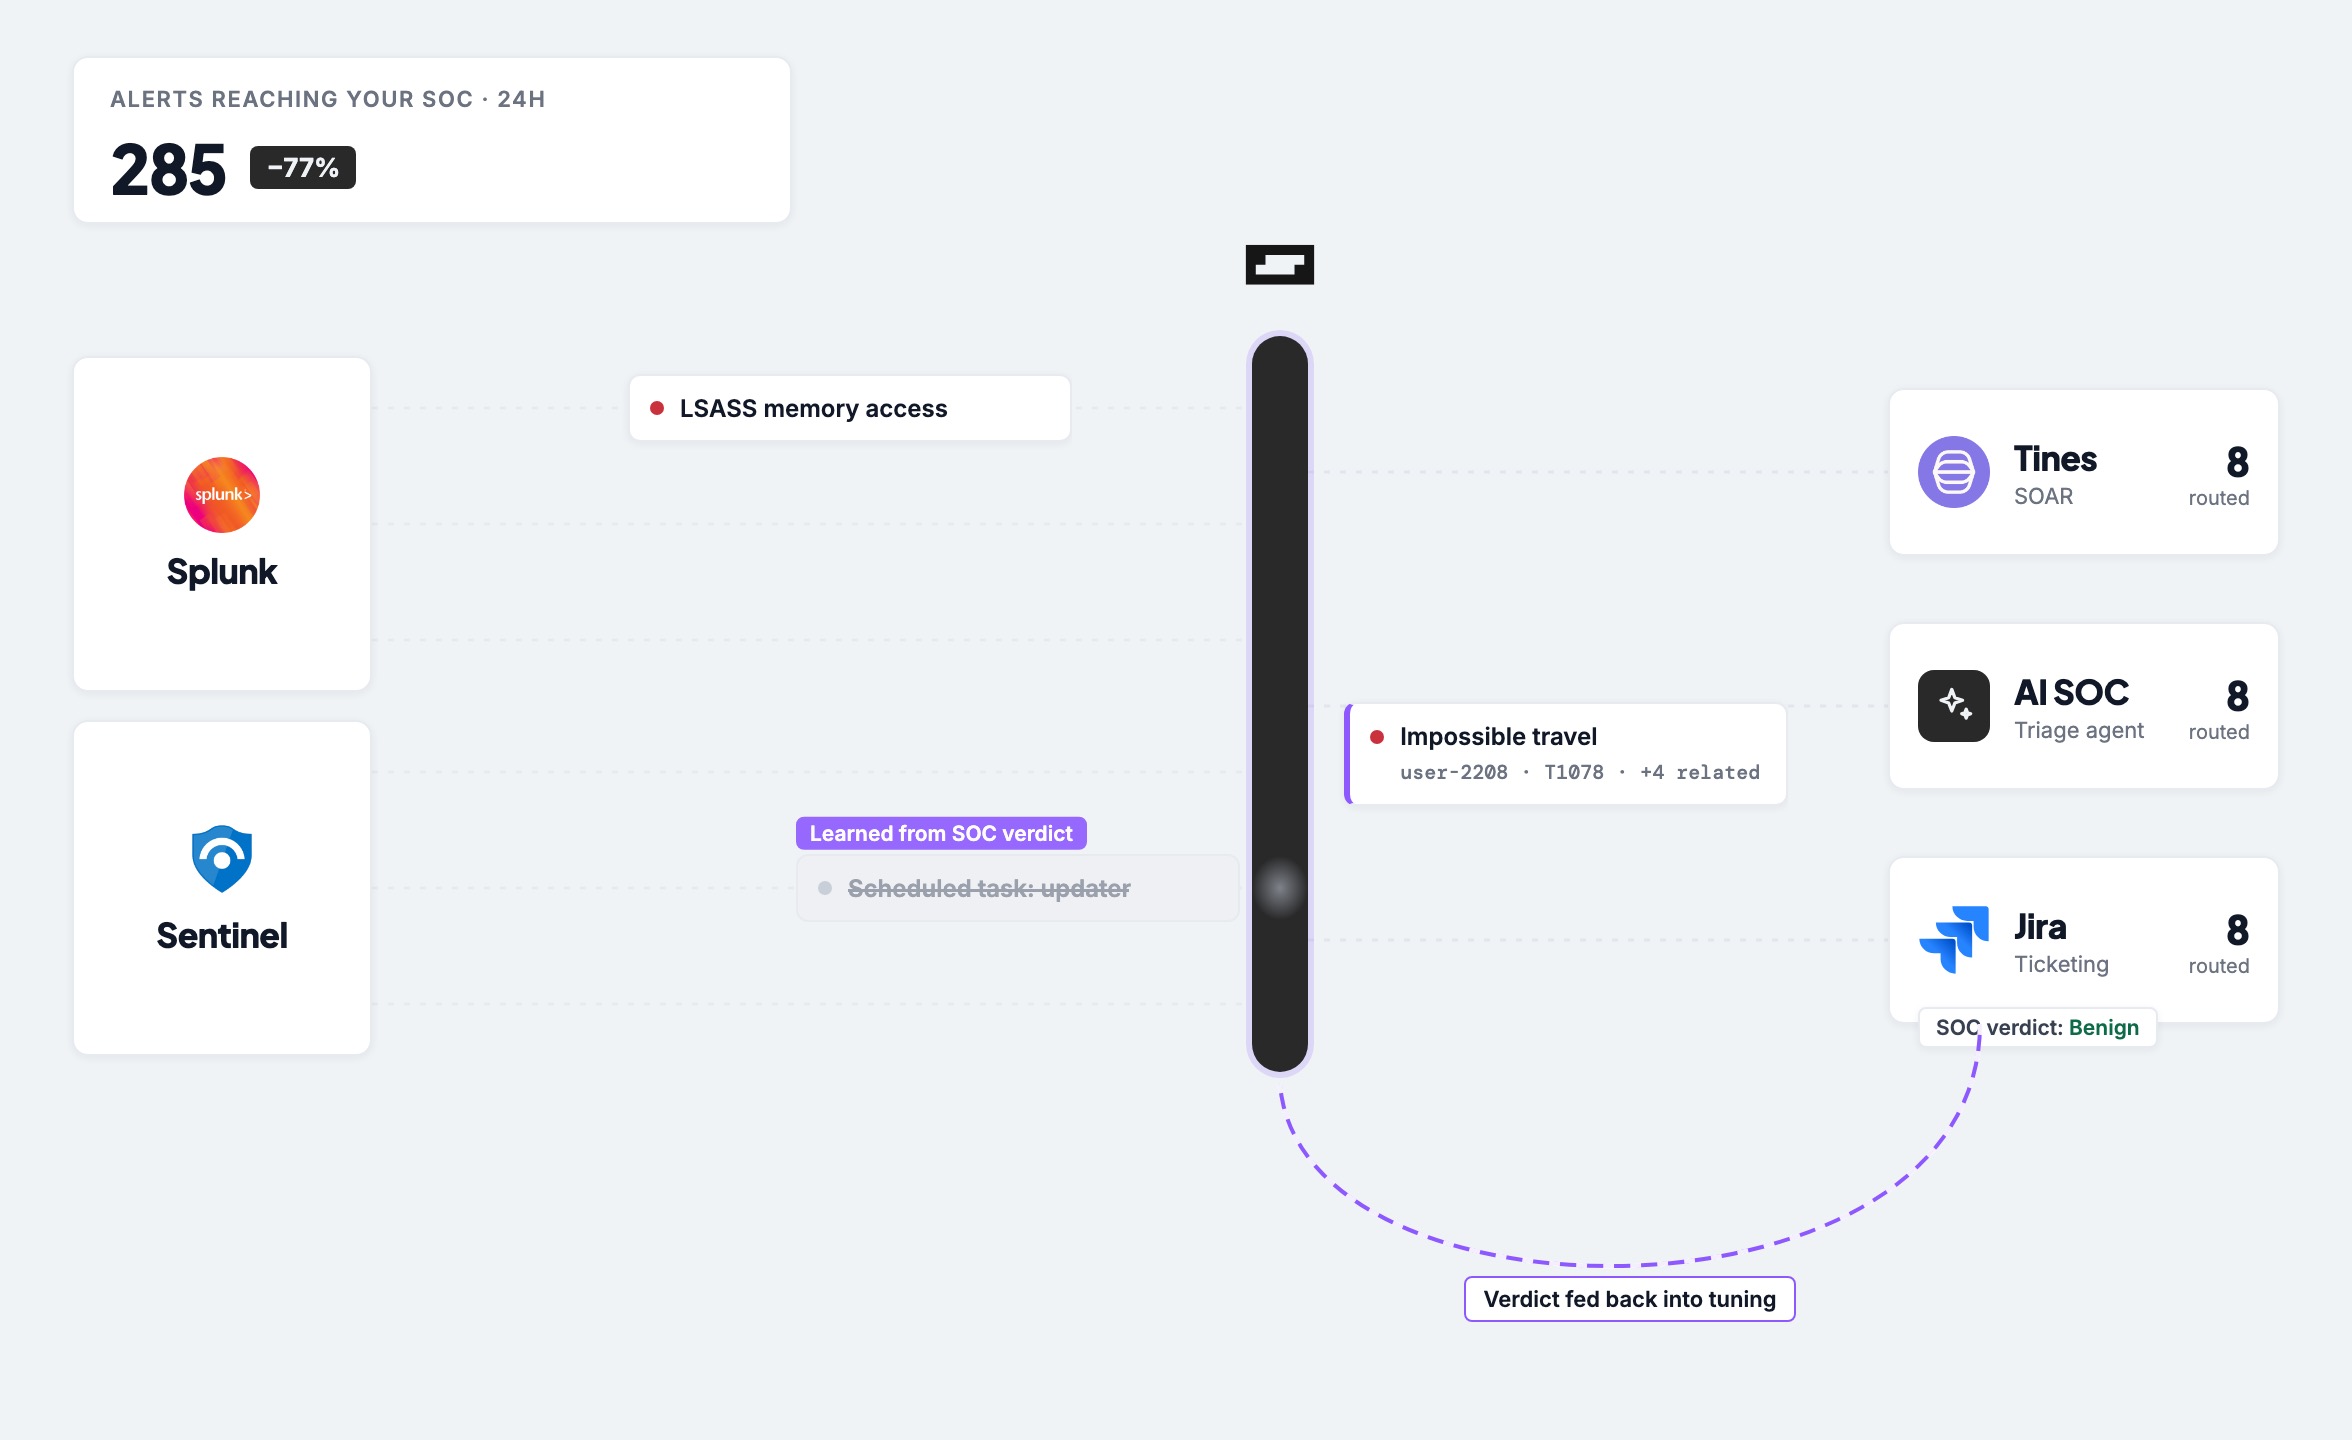
If it fires, it matters
Cut noise and deliver feedback, making each alert relevant.
- Reduce noise without weakening coverage
- Automatically tune noisy or failing rules
- Make every alert relevant and worth reviewing
Works with the stack you have
No rip & replace: Spectrum connects to the tools you already run, and carries your detections and data strategy across when you change them.
- Splunk
- CrowdStrike
 Snowflake
 Google BigQuery
 SentinelOne
 Recorded Future
 Bitbucket
 Tines
- Microsoft Sentinel
 Sumo Logic
 Amazon Security Lake
 Bindplane
 Google Threat Intelligence
 GitLab
- Torq
- Jira
- Google SecOps
- Elastic
 Databricks
- Cribl
 Microsoft Defender
 OpenCTI
 GitHub
- Cortex XSOAR
 ServiceNow
Key Customer Use Cases
Threat Intel to Detection, Automatically
Less Noise. Sharper Signal.
Cut SIEM Spend, Not Coverage
SecOps Health & Resilience
SIEM Migration
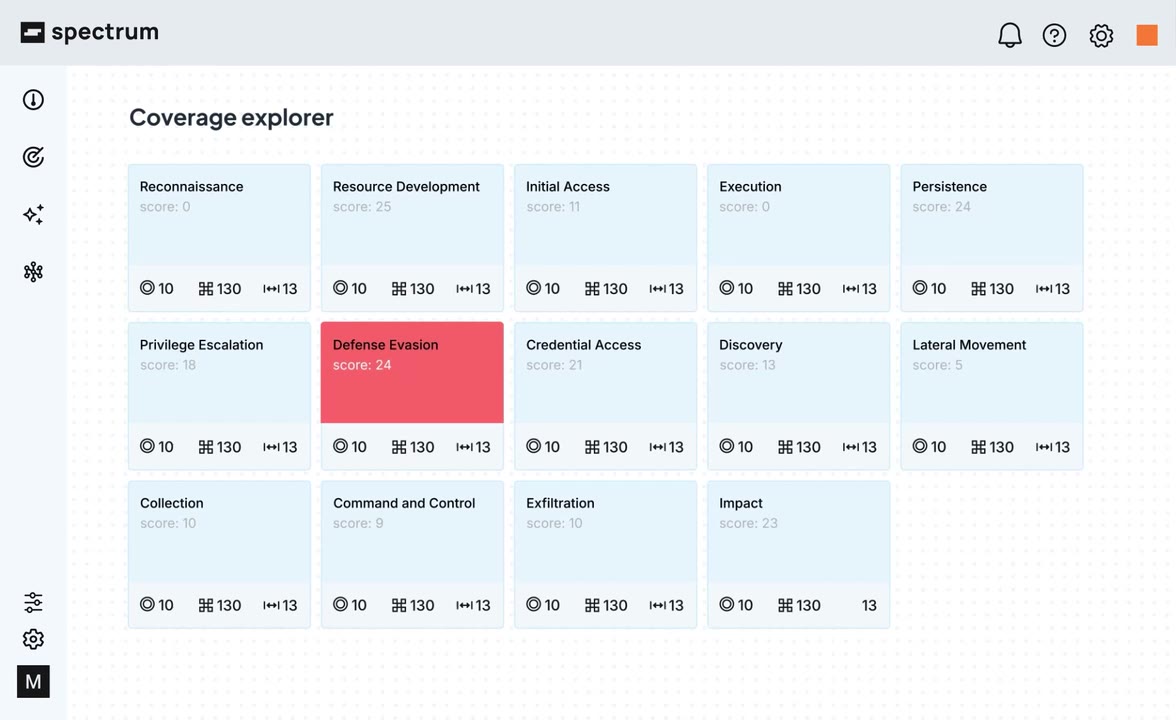
Full Coverage Visibility & Reporting
1/3
SecOps at machine speed lets us keep up with threats. With Spectrum, the endless backlog and manual grind are finally gone.
Head of SecOps
Global Technology Company