early access insights, threat research, and the latest on autonomous security.
We've been organizing security operations around our tools instead of around the threat. Spectrum is now one brain across your SIEM, data pipeline, edge detection, response and ticketing tools, for better coverage, less noise and a lower SIEM bill.
Spectrum
Learn more
A trojanized copy of the OnionClaw agent skill hid a Lua loader in a ZIP. Following it through a Polygon smart contract, two GitHub-hosted tasks and a second loader ends at a StealC v2-family infostealer. Every layer, and the indicators to hunt.
Anthony Jirouschek
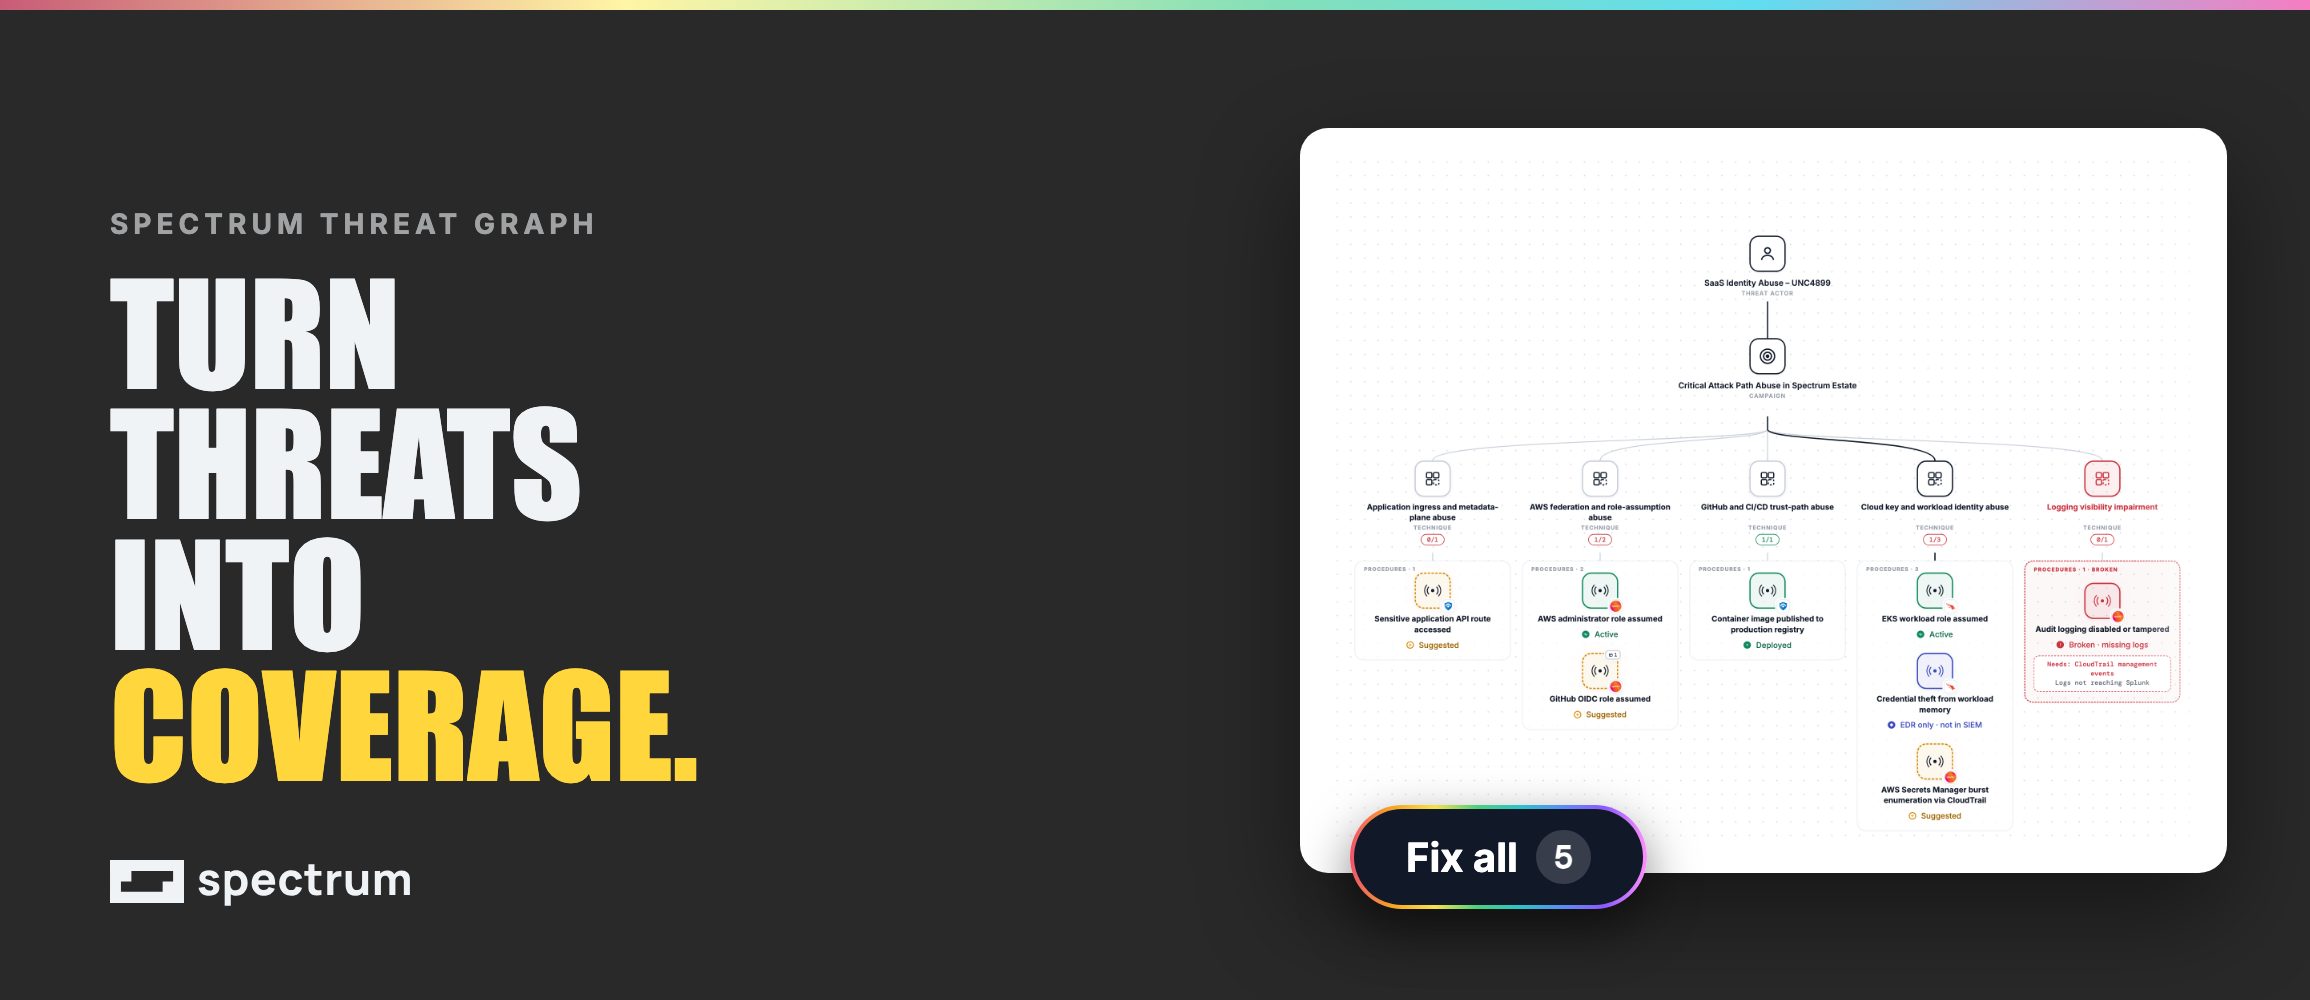
A new threat surfaces. Is it relevant to you, and can you detect it? Spectrum checks every new threat against the technologies in your environment, maps the ones that apply in the Threat Graph, and shows your real coverage procedure by procedure across your SIEMs and EDR.
A phishing kit that streams you a real Google sign-in from the attacker's own browser, so your password and MFA approval land in their session. How it works, how to clean up after it, and the Google SecOps detections that catch it.
A broken rule and a working rule look identical: both are either firing or they aren't. Spectrum checks every detection in your estate daily, validates the dependencies each rule needs against live data, returns a verdict with a root cause, and automatically fixes the detection — all in minutes.
Anthony Jirouschek and Dylan Williams take apart the Delta team's MCP research: six working attacks against real MCP servers, why the same attack lands differently depending on which SDK you built on, and what each one leaves behind for a detection engineer to catch.
MCP is a USB port for your AI agent - but it is also a new standard ripe for attacks. Here I describe six attacks against real MCP servers built on TypeScript and Python SDKs. The takeaway? MCP security is per-SDK, not per-spec.
SEP2 runs a 24/7 MDR service across more than 70 customers, from AI-native startups to legacy public sector estates. By automating detection engineering with Spectrum during its build phase, SEP2 cut rapid-response rule deployment time by 66% and doubled its deployed detections with no additional headcount.
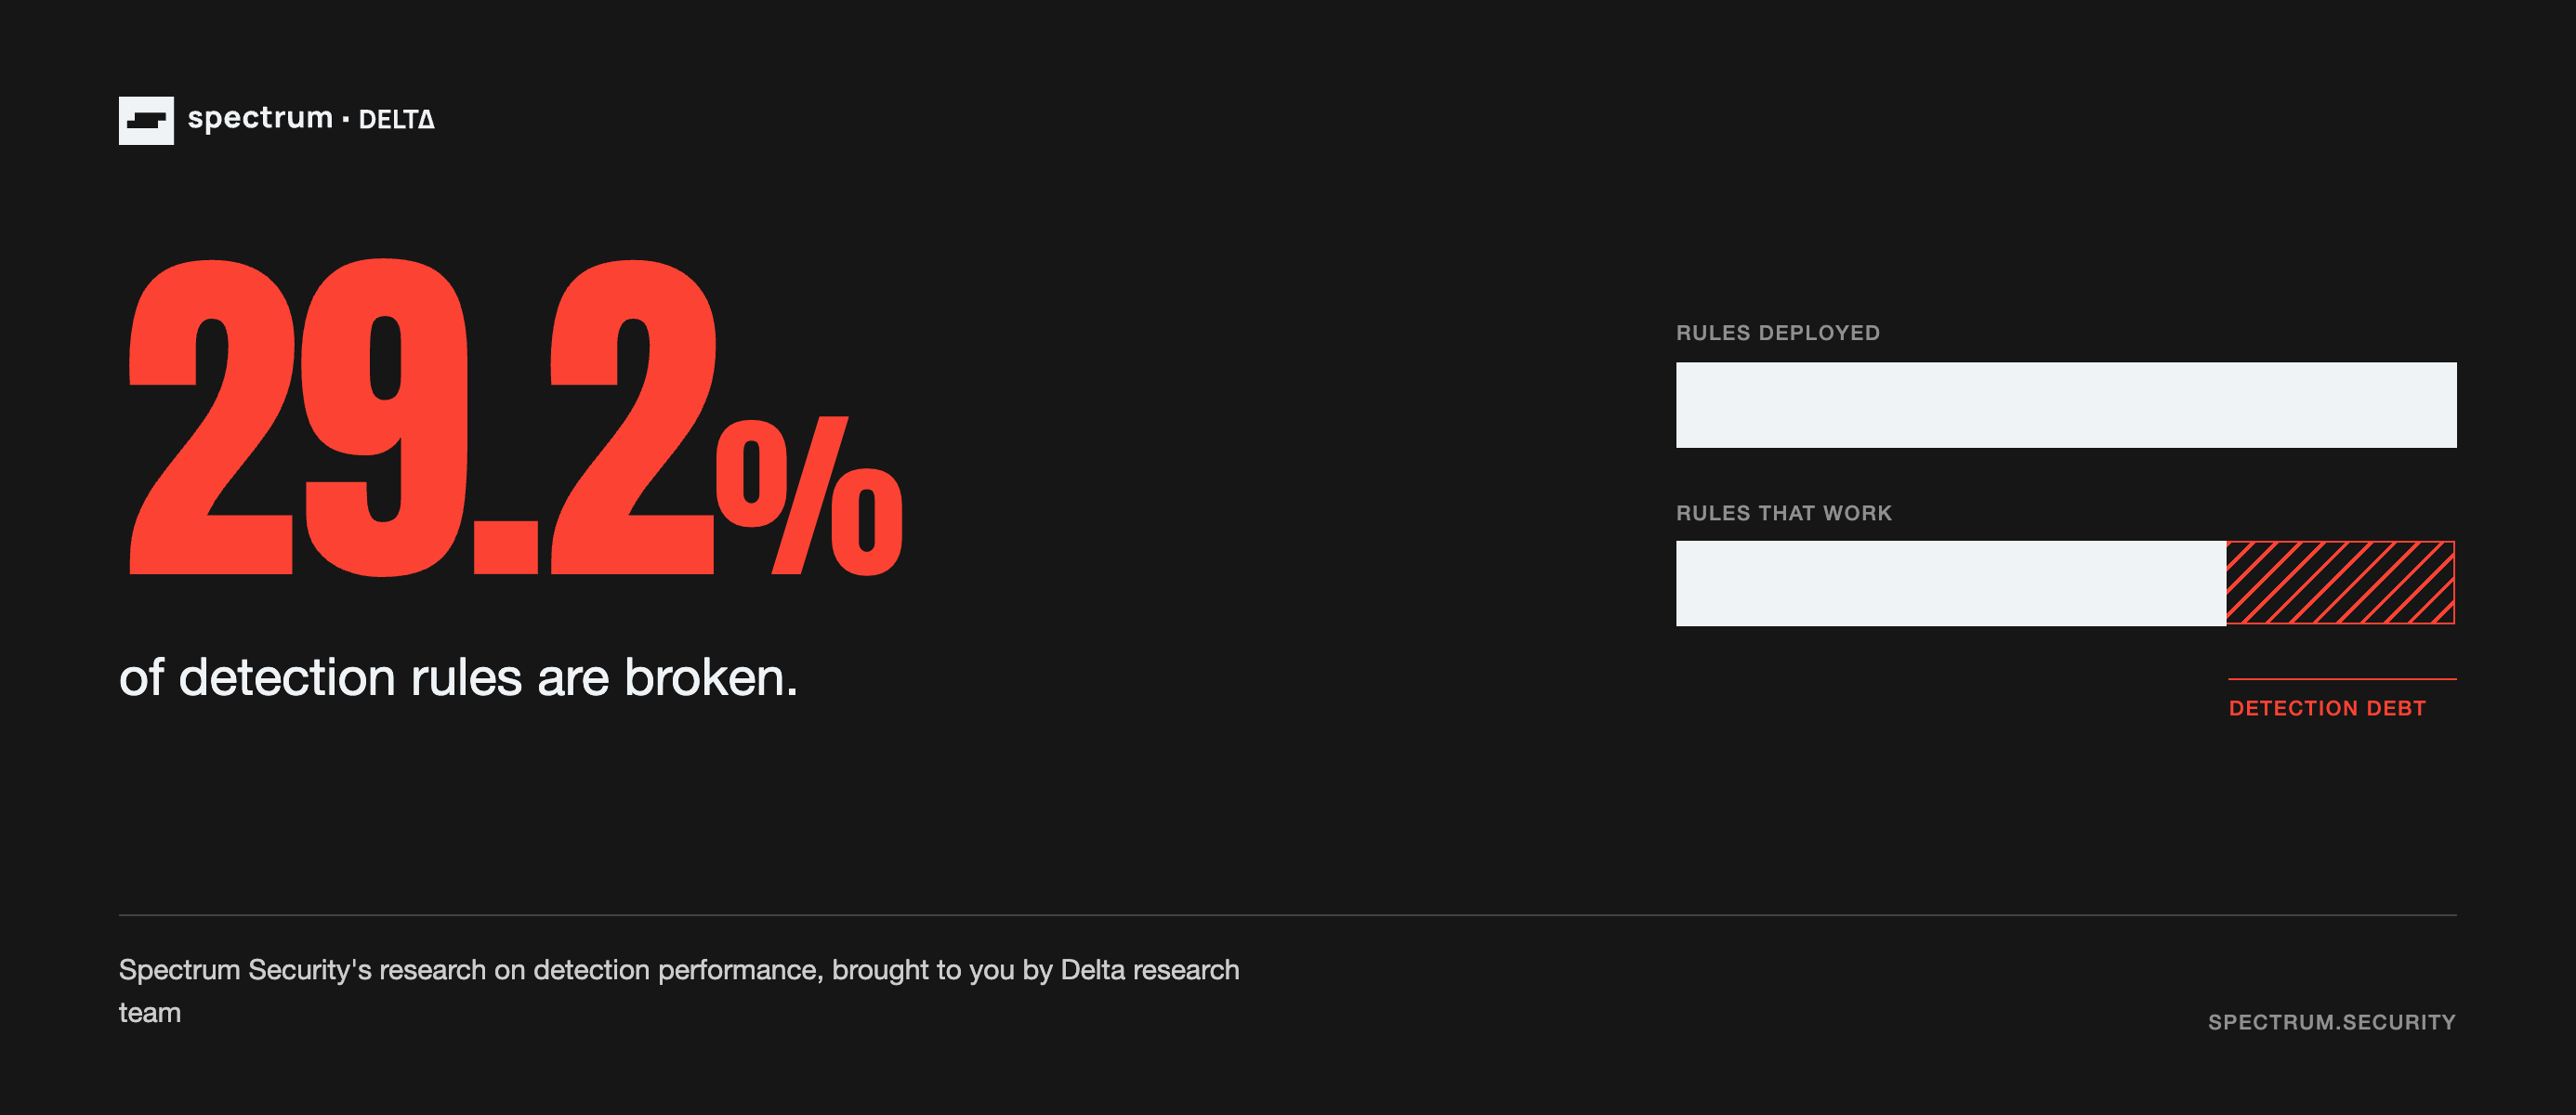
Nearly 3 in 10 deployed detection rules are broken. We verified detection estates across six SIEM platforms against customers' live systems — not exported rule files — and replayed the broken ones to count the alerts nobody ever saw.
Our end-to-end agentic research pipeline is generally available: Spectrum continuously researches the threats that can actually reach your environment, and turns that research into detection-ready findings.
Chris Reuter
Security leaders sound off on AI adoption in detection
Detection logic is cheap; detection knowledge isn't. Delta Tradecraft is an open standard for capturing the research behind a detection so it's reusable.
Dylan Williams
Meet Delta, Spectrum Security's research team: a skunkworks for autonomous detection engineering and AI threat hunting, publishing its work in the open.
An AI broke out of an OpenAI benchmark and breached Hugging Face with attacks no signature could match. How it was detected holds a lesson for every CISO.
Detection is the layer everything depends on, and nobody has modernized it. Today we launch Spectrum to change that.
Meny Har
Led by TechOperators alongside WhiteRabbit Ventures, Skinos Ventures (by Shlomo Kramer), and Alumni Ventures, Spectrum automates threat detection at machine speed.
Data collection is not detection. After a decade of hoarding logs and relying on manual engineering, security teams are still guessing at their coverage. We are building the future of detection to replace uncertainty with proof
Why traditional detection models fail to keep up with dynamic threats and how AI-driven continuous detection engineering is closing the coverage gap
Visibility is not coverage. After decades of manual engineering and 'heroic' efforts, the pieces are finally in place to solve the detection gap. Introducing Spectrum.
John DiFederico
 October 20, 2026